Migrate to Full Permissions
Clusters imported in read-only mode can be migrated to full permission mode at any time. Migrating upgrades the Palette agent's Role-Based Access Control (RBAC) permissions, which enables additional Day-2 operations such as deploying add-on profiles, configuring RBAC bindings, running compliance scans, and scheduling backups. The agent also automatically installs a metrics server if one is not already present on the cluster. For a full comparison of what each mode supports, refer to Import Modes.
Prerequisites
-
An imported cluster in read-only mode. Refer to the Import a Cluster guide to learn how to import a cluster into Palette.
-
kubectl installed on your local workstation and configured to access your imported cluster.
Migrate to Full Permissions
-
Log in to Palette.
-
From the left main menu, select Clusters.
-
Select your imported read-only cluster from the Clusters table.
-
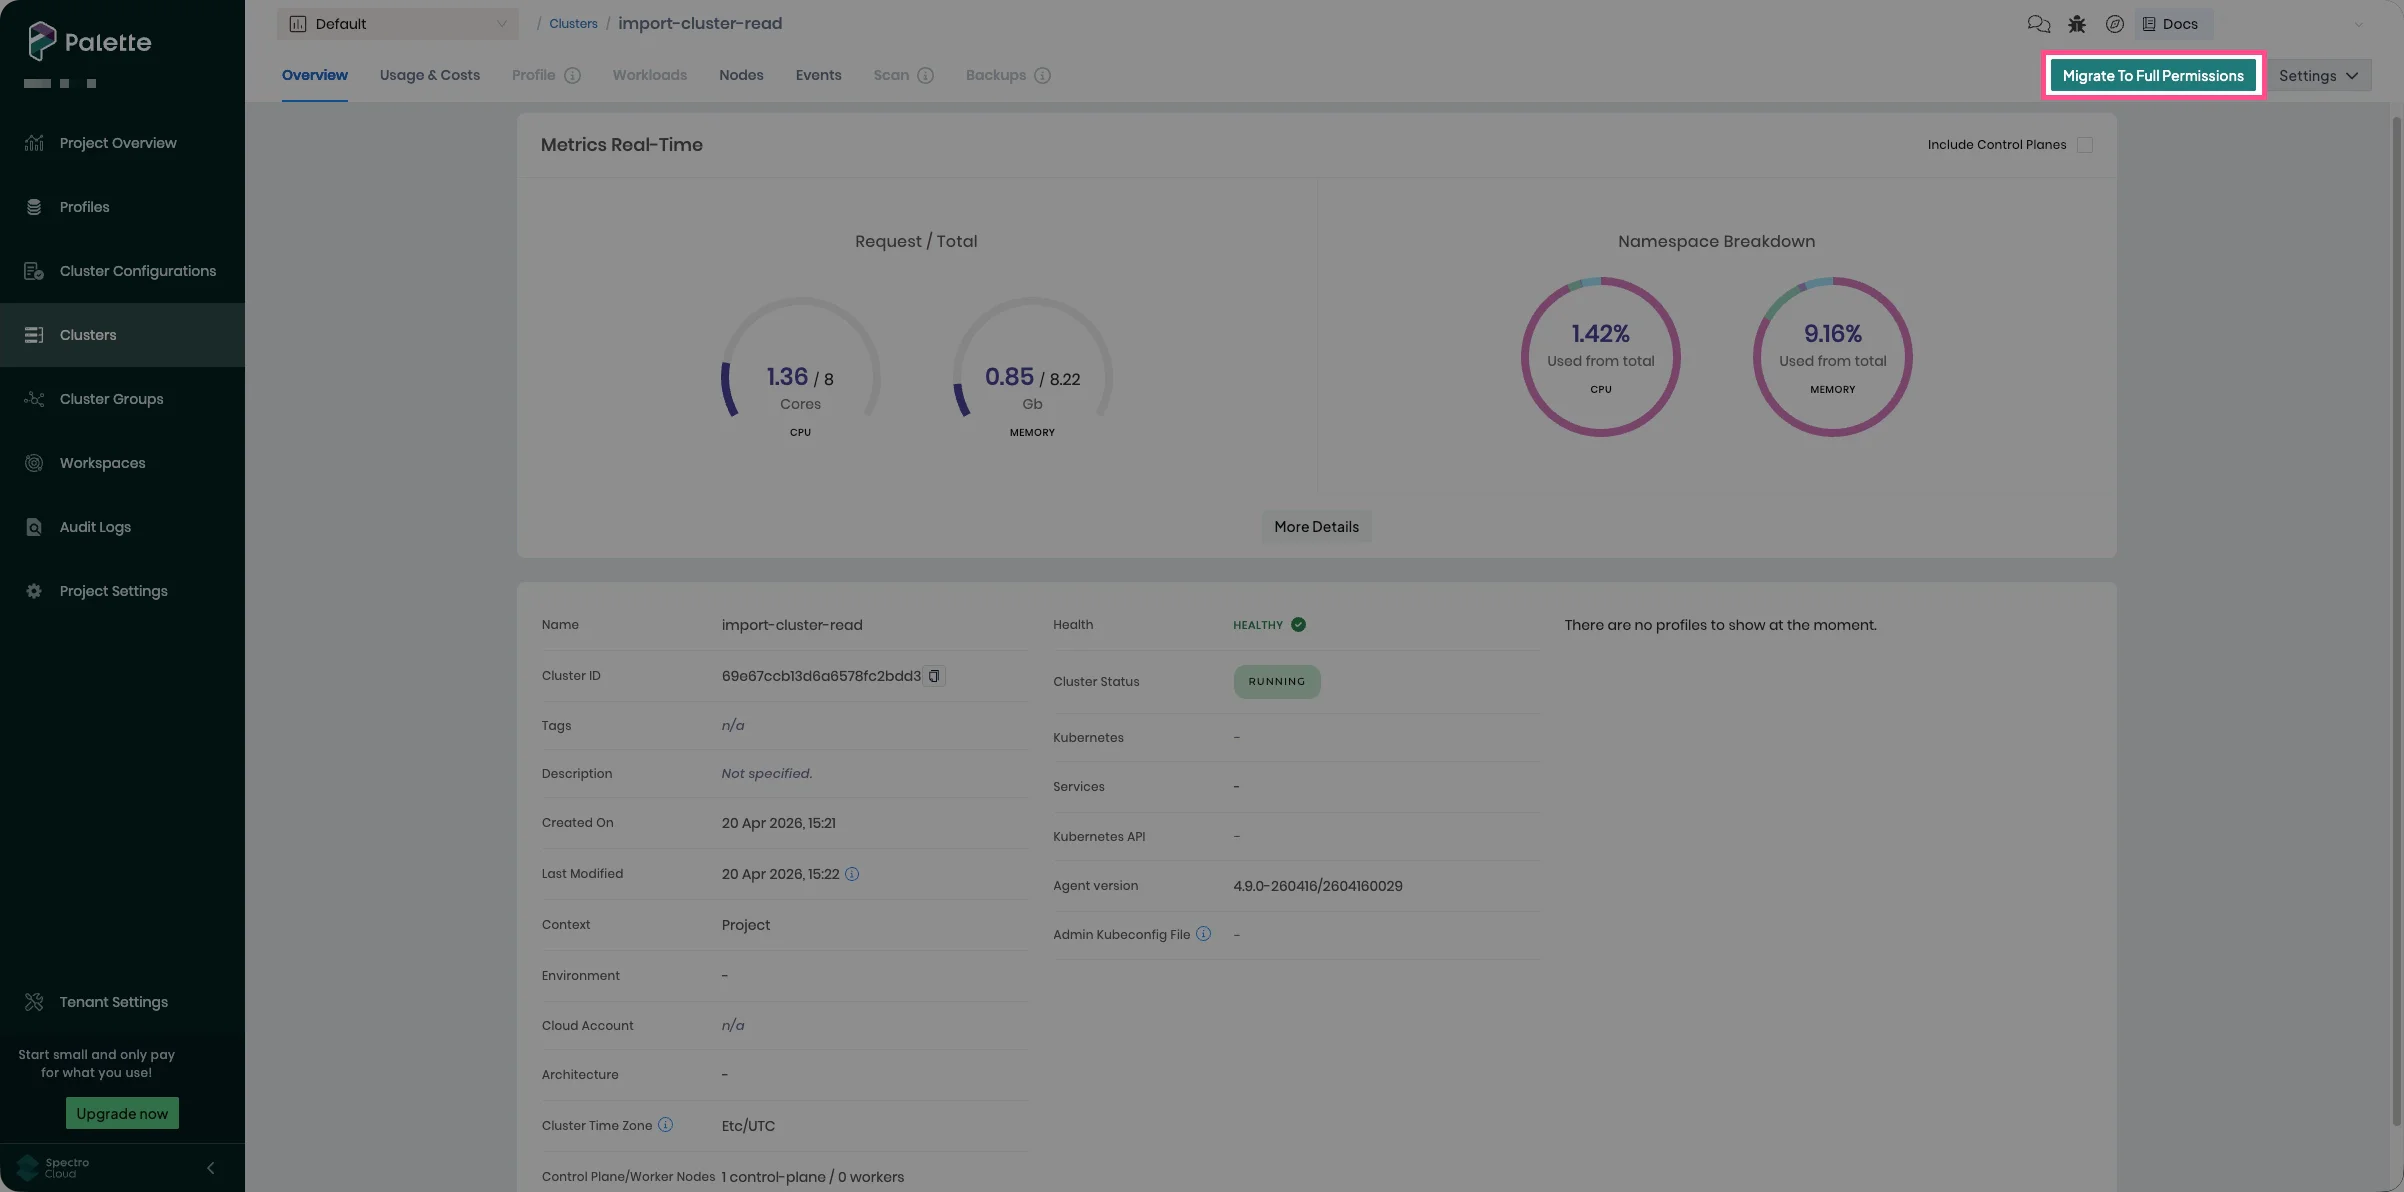
On the cluster Overview tab, select Migrate To Full Permissions.
-
Select OK to begin the migration process.
-
You are redirected to the imported cluster's Overview tab. A set of instructions with commands is displayed on the drawer. You must issue the following commands to complete the import process.
-
Select Download manifest.
infoOnce you select Download manifest, the cluster status transitions to Importing. If you close the drawer and later discover the download was blocked or did not complete, the drawer will not reopen. In this case, you must fetch the manifest using the Palette API endpoint
/v1/spectroclusters/<uid>/import/manifest.Retrieve Manifest Manually
Replace the placeholders in the following commands with the appropriate values.
Parameter Description <palette-endpoint>The endpoint of your Palette instance. <cluster-uid>The unique ID assigned to imported cluster. Found at Clusters > [Cluster] > Cluster ID. <api-key>Your Palette API Key. <project-uid>(Project scope only) The Palette project you are importing your cluster to. Found in the top-right on the Project Overview. This field is not applicable in the Tenant Admin scope. <jwt-token>Your Palette Authorization Token. - API Key
- JWT Token
Omit the line
--header "ProjectUid: <project-uid>" \if you are importing the cluster in the Tenant Admin scope.curl --silent --show-error --request GET \
"https://<palette-endpoint>/v1/spectroclusters/<cluster-uid>/import/manifest" \
--header "ApiKey: <api-key>" \
--header "ProjectUid: <project-uid>" \
--output "cluster-<cluster-uid>-manifest.yaml"curl --silent --show-error --request GET \
"https://<palette-endpoint>/v1/spectroclusters/<cluster-uid>/import/manifest" \
--header "Authorization: <jwt-token>" \
--output "cluster-<cluster-uid>-manifest.yaml" -
Open a terminal on your local workstation and verify you are in the correct Kubernetes context. Expand the following section for guidance on changing your context.
kubectl config current-contextExample outputkind-import-cluster-fullSwitch Kubernetes Context
If you are not in the correct Kubernetes context, switch to the proper context so you are interacting with the correct imported cluster when using kubectl. To do so, verify the contexts available in your current kubeconfig file. Your current context is indicated with an asterisk (
*).kubectl config get-contextsExample outputCURRENT NAME CLUSTER AUTHINFO NAMESPACE
* kind-import-cluster-full kind-import-cluster-full kind-import-cluster-full default
kind-import-cluster-read kind-import-cluster-read kind-import-cluster-palette defaultUse the following command to switch to the appropriate context.
kubectl config use-context <context-name>If the desired context is not part of your current kubeconfig file, set the
KUBECONFIGvariable to the path that contains the correct context, and set the context.export KUBECONFIG=<path-to-kubeconfig>
kubectl config use-context <context-name> -
Apply the manifest to your Kubernetes cluster using the appropriate download path to start the migration.
kubectl apply --filename <path-to-download>/manifest.yamlExample outputnamespace/cluster-69e67ccb13d6a6578fc2bdd3 configured
customresourcedefinition.apiextensions.k8s.io/awscloudconfigs.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/azurecloudconfigs.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/cloudstackcloudconfigs.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/clusterprofiles.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/customcloudconfigs.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/edgecloudconfigs.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/edgenativecloudconfigs.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/gcpcloudconfigs.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/maascloudconfigs.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/nestedcloudconfigs.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/packs.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/spectroclusters.cluster.spectrocloud.com configured
customresourcedefinition.apiextensions.k8s.io/vspherecloudconfigs.cluster.spectrocloud.com configured
serviceaccount/palette-manager created
clusterrolebinding.rbac.authorization.k8s.io/palette-lite-cluster-admin-binding configured
configmap/palette-version-info-g7bkcc8gf2 created
priorityclass.scheduling.k8s.io/palette-spectro-cluster-critical configured
deployment.apps/palette-lite-controller-manager created
job.batch/palette-import-presetup-job created
serviceaccount/cluster-management-agent unchanged
clusterrole.rbac.authorization.k8s.io/cma-lite-cluster-least-privilege-role unchanged
clusterrolebinding.rbac.authorization.k8s.io/cma-lite-cluster-least-privilege-binding configured
configmap/log-parser-config unchanged
configmap/upgrade-info-5tgb8c4chb unchanged
configmap/version-info-5hkbtbgh44 unchanged
priorityclass.scheduling.k8s.io/spectro-cluster-critical configured
deployment.apps/cluster-management-agent-lite configured
configmap/cluster-info unchanged
configmap/hubble-info unchanged
secret/hubble-secrets configured -
The drawer disappears, and the Profile, Workloads, Scan, and Backups tabs are unlocked.
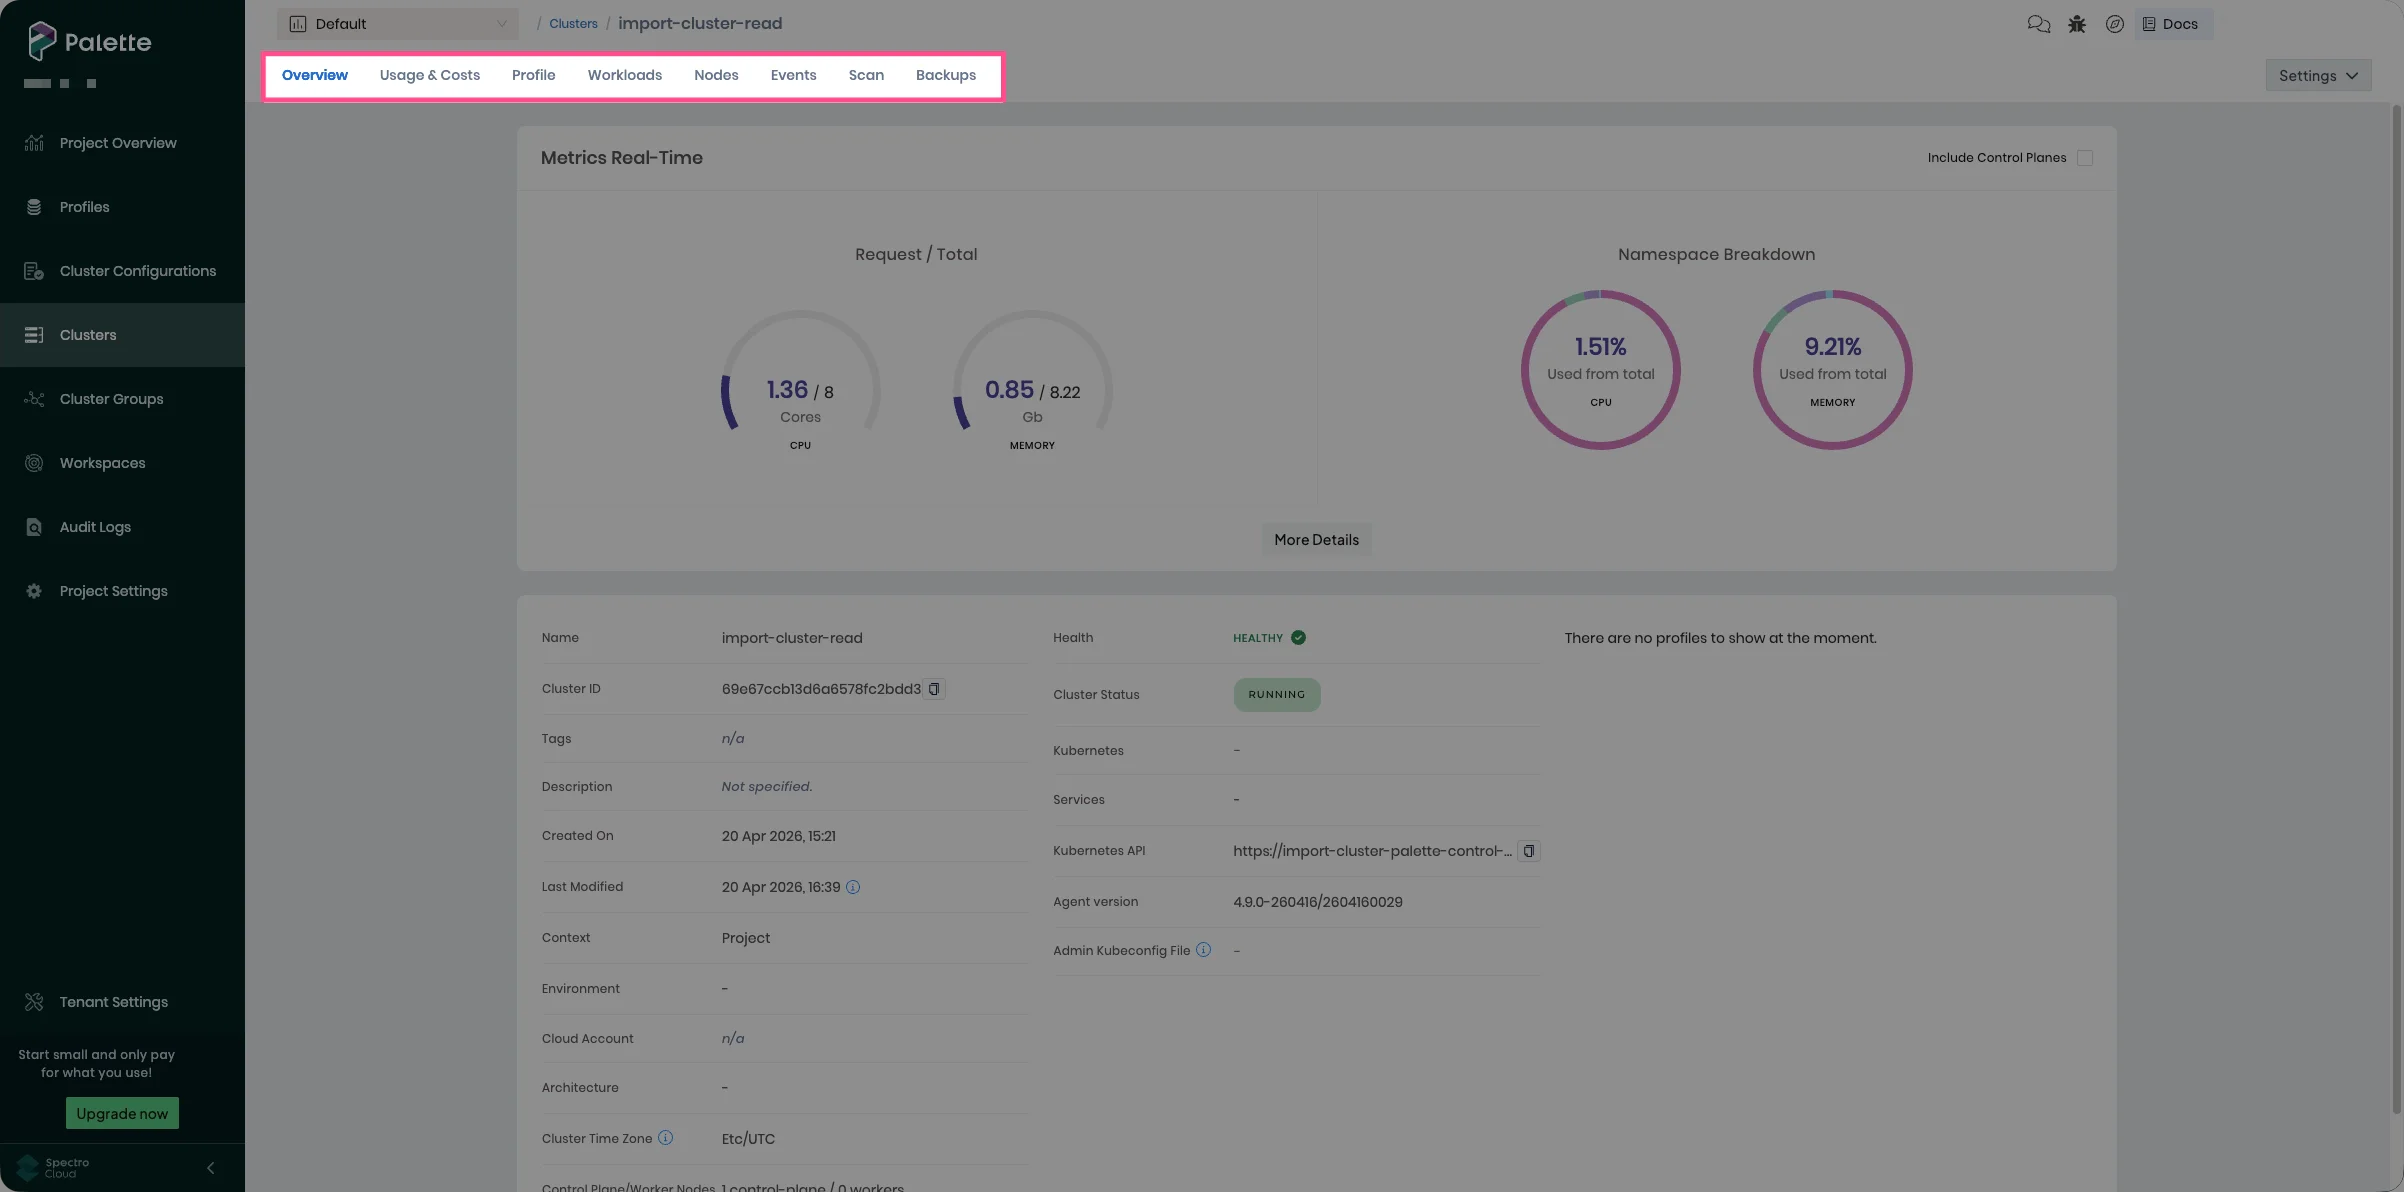
You have successfully migrated a read-only mode cluster to full permission mode.
Validate
-
Log in to Palette.
-
From the left main menu, select Clusters.
-
From the Clusters table, select your imported cluster.
-
Verify that you can interact with the Profile, Workloads, Scan, and Backups tabs. The Migrate To Full Permissions button should also no longer be available.
Next Steps
Imported clusters in full permission mode allow you to perform additional Day-2 activities through Palette. You can also deploy add-on cluster profiles to build upon your cluster's current functionality. Refer to the Attach an Add-on Profile guide to learn more.