Create Source Providers
Follow this guide to create source providers using the VM Migration Assistant. Source providers host the Virtual Machines (VMs) that need to be migrated.
Prerequisites
- The Virtual Machine Migration Assistant pack must be added to your cluster profile. Refer to Create a VM Migration Assistant Cluster Profile for guidance.
-
The VM Migration Assistant service console must be accessible from a web browser.
-
A healthy Virtual Machine Orchestrator (VMO) cluster. Refer to the Create a VMO Profile for further guidance.
- The VMO cluster must have network connectivity to vCenter and ESXi hosts, and the VMs you want to migrate.
-
A vCenter user account with the following necessary privileges to perform migrations.
Privileges Description Virtual Machine Interaction Privileges (all) Allow creating, cloning, modifying, customizing, and managing templates, virtual machines, their files, and customization specifications, as well as performing disk and deployment-related operations. Virtual machine.Snapshot management.Create snapshot Allows capturing the current state of a virtual machine as a snapshot. Virtual machine.Snapshot management.Remove Snapshot Permits deletion of a snapshot from the snapshot history. -
If you want to browse resources using the vCenter UI, you may require additional privileges. Refer to the Required vCenter Server Privileges for Common Tasks documentation for more information.
-
Migrations can be optionally accelerated by providing credentials for the ESXi hosts where the VMs reside.
-
-
One or more VMs hosted in VMware vSphere 7.0 or 8.0. The VM's OS must be present in the virt-v2v supported guest systems list.
- For cold migrations, ensure that VMs operating Windows are shut down at the guest OS level.
- For warm migrations, Changed Block Tracking must be enabled on your VMs.
-
A VMware Virtual Disk Development Kit (VDDK) image is required for migrations. The migration engine uses VDDK on the destination VMO cluster to read virtual disks from the source environment, transfer the data, and write it to the target storage.
warningBroadcom no longer offers public VDDK downloads. Downloading VDDK requires a Broadcom account with the appropriate product entitlements and an active vSphere subscription. If you cannot access the download, contact your Broadcom account team or support representative.
-
Use VDDK 9. The migration engine supports VDDK 9 for migrating source VMs from VMware vSphere 7.0 and 8.0.
-
You must build and host the VDDK image in your own image registry, which must be accessible to the destination VMO cluster for migrations.
Example steps to build and upload VDDK image
- Non-Airgap
- Airgap
-
Download the VDDK image from the Broadcom Developer Portal. A Broadcom account with the appropriate product entitlements is required.
-
Decompress the downloaded image.
tar -xzf VMware-vix-disklib-<version>.x86_64.tar.gz -
Create a Dockerfile to build the VDDK image.
cat > Dockerfile <<EOF
FROM <myregistry/myrepository:tag>
USER 1001
COPY vmware-vix-disklib-distrib /vmware-vix-disklib-distrib
RUN mkdir -p /opt
ENTRYPOINT ["cp", "-r", "/vmware-vix-disklib-distrib", "/opt"]
EOF
Replace the
<myregistry/myrepository:tag>with your chosen base image registry, repository, and tag (for example:ubuntu:22.04). -
Build the image.
docker buildx build --platform linux/amd64 --tag <docker-registry>/vddk:<tag> . -
Push the built image to your image registry.
docker push <docker-registry>/vddk:<tag>
-
Download the VDDK image from the Broadcom Developer Portal. A Broadcom account with the appropriate product entitlements is required.
-
Copy or move the VDDK image to another Linux environment inside your airgap environment.
-
Log in to the Linux environment inside your airgap environment where you copied the VDDK image.
-
Decompress the downloaded image.
tar -xzf VMware-vix-disklib-<version>.x86_64.tar.gz -
Create a Dockerfile to build the VDDK image.
cat > Dockerfile <<EOF
FROM <myregistry/myrepository:tag>
USER 1001
COPY vmware-vix-disklib-distrib /vmware-vix-disklib-distrib
RUN mkdir -p /opt
ENTRYPOINT ["cp", "-r", "/vmware-vix-disklib-distrib", "/opt"]
EOF
Replace the
<myregistry/myrepository:tag>with your chosen base image registry, repository, and tag (for example:ubuntu:22.04). -
Authenticate with your OCI registry. The following examples are for Harbor and AWS ECR.
- Harbor
- AWS ECR
Use
orasto log in to your OCI registry. Replace<username>and<password>with your registry credentials, and replace<harbor-address>with your Harbor hostname / IP address. Check out the oras login documentation for information about additional CLI flags and examples.oras login <harbor-address> --username '<username>' --password '<password>'If you are using a Harbor registry with a self-signed certificate, add the
--insecureflag to theorascommand.oras login <harbor-address> --insecure --username '<username>' --password '<password>'Acquire the AWS ECR authentication command from the AWS ECR console. From the ECR repository details page, click on the View push commands button to access the command. Refer to the AWS ECR Authentication documentation for more information.
Use the following command to authenticate with AWS ECR. The output of the
awscommand is passed toorasto authenticate with the ECR registry. Replace<username>with your registry username and<aws-ecr-url>with your registry URL. Enter your registry password when prompted.aws ecr get-login-password --region xxxxx | oras login --username <username> --password-stdin <aws-ecr-url>For a public image repository, use the
dockerCLI instead oforas. Replace<username>with your registry username and<aws-ecr-url>with your registry URL. Enter your registry password when prompted.aws ecr-public get-login-password --region xxxxx | docker login --username <username> --password-stdin <aws-ecr-url> -
Build the image.
- Harbor
- AWS ECR
Replace
<harbor-address>with your Harbor hostname / IP address,<project-name>with the target project name in Harbor, and<tag>with your chosen image tag.docker buildx build --platform linux/amd64 --tag <harbor-address>/<project-name>/vddk:<tag> .Replace
<aws-ecr-url>with your registry URL and<tag>with your chosen image tag.docker buildx build --platform linux/amd64 --tag <aws-ecr-url>:<tag> . -
Push the built image to your image registry.
- Harbor
- AWS ECR
Replace
<harbor-address>with your Harbor hostname / IP address,<project-name>with the target project name in Harbor, and<tag>with your chosen image tag.docker push <harbor-address>/<project-name>/vddk:<tag>Replace
<aws-ecr-url>with your registry URL and<tag>with your chosen image tag.docker push <aws-ecr-url>:<tag>
-
If you are using a private image registry, you must create a Secret to be used for the migration. The Secret must be created in the namespace where the VMs will be migrated to, and the
metadata.namevalue must bevddk-image-pull-secret.Example Secret Creation
You can create a Secret by issuing the following command.
kubectl create secret docker-registry vddk-image-pull-secret \
  --docker-server=myRegistryServer \
  --docker-username=myUsername \
  --docker-password=myPassword \
  --docker-email=myEmail \
  --kubeconfig=/path/to/myKubeconfig \
  --namespace=myVmMigrationNamespace \
  --output yaml
This creates the Secret named
vddk-image-pull-secretin your destination cluster under the namespace provided. Ensure that this namespace matches the one you have chosen for the VM migration.apiVersion: v1
kind: Secret
metadata:
name: vddk-image-pull-secret
data:
.dockerconfigjson: #base64-encoded dockerconfigjson
type: kubernetes.io/dockerconfigjsonThe
data.dockerconfigjsonvalue contains your registry credentials, which have been base64-encoded by the command.Alternatively, you can manually encode a
config.jsonby issuing the following command.cat path/to/config.json | base64 --wrap=0Example outputeyJodHRwczovL2luZGV4L ... J0QUl6RTIifX0=You can then use this output to create your own Secret manually. Ensure that the
metadata.nameis set tovddk-image-pull-secret.Refer to the Pull an Image from a Private Registry and kubectl create secret docker-registry documentation for additional guidance.
-
Create Source Provider
-
From the left main menu, select Providers, then click Create provider in the top-right corner.
-
On the Create provider page, select the Provider namespace from the drop-down.
The provider namespace is the Kubernetes namespace where the provider credentials and configuration will be stored. This should be the same namespace where you plan to migrate your VMs to.
-
Select the VMware vSphere from the Provider type drop-down. Once you select a provider type, additional fields appear. The following table describes the details to fill in for the provider.
warningThe Open Virtual Appliance (OVA) provider type is not supported.
Provider Settings
Setting Description Provider name A unique name for your provider. vSphere endpoint Select the type of endpoint to configure the connection. Choose vCenter if managing multiple hosts through a central server, or ESXi if connecting directly to a standalone host. API endpoint URL Your vSphere / ESXi API endpoint for the software development kit (SDK). You can specify a Fully Qualified Domain Name (FQDN) or an IP address. For example, https://vcenter.mycompany.com/sdk.Virtual Disk Development Kit (VDDK) setup Select the option to Manually specify the VDDK image URL. A VDDK image is required for VM migrations. Refer to the Prerequisites for more information. Upload a VDDK archive to generate the image URL Unsupported method. Manually specify the VDDK image URL Provide the registry URL to the VDDK image in the VDDK init image field. Specify the registry URL without the HTTP scheme https://orhttp://. For example,docker.io/myorganization/vddk:v8.0.3.Use VMware Virtual Disk Development Kit (VDDK) async IO Optimization When enabled, this option uses asynchronous input/output operations to process multiple disk read/write requests simultaneously during VM migration, rather than sequentially. This can significantly improve disk transfer speeds, particularly for environments with high-latency storage or high-bandwidth networks, but increases memory usage on the VMware ESXi host's Network File Copy (NFC) server. Convert Disk When enabled, disk conversion is handled using virt-v2v. For example, if you are migrating from VMware vSphere to VMO, virt-v2v can convert Virtual Machine Disk (VMDK) to raw or QEMU copy-on-write version 2 (qcow2) formats that are optimal for the target environment. When disabled, disks are transferred using raw copy mode. This option appears after the Provider Credentials. Provider Credentials
Setting Description Username Your vSphere / ESXi account username. For example, user@vsphere.local.Password Your vSphere / ESXi account password. Certificate validation Configure certificate validation for your vSphere / ESXi provider or Skip certificate validation. Configure certificate validation Upload or drag and drop the certificate authority (CA) certificate for your vSphere / ESXi. Skip certificate validation Enabling this option bypasses x509 CA verification. -
Click Create Provider.
-
On the provider details page, if you need to change a setting, click the Edit icon next to each value and adjust it in the pop-up window. Click Save after making changes.
If you want to explore additional settings, refer to Additional Configuration - Provider Settings for guidance.
Validate
-
From the left main menu, select Providers.
-
All namespaces are displayed by default. If you want to view a specific namespace, use the Namespace drop-down in the top-left corner to select your Kubernetes namespace for the migration.
-
Find your provider in the table and click the provider name to view its details. You can use the table filters to help locate your provider if needed.
-
On the Details tab, the provider status displays as Ready.
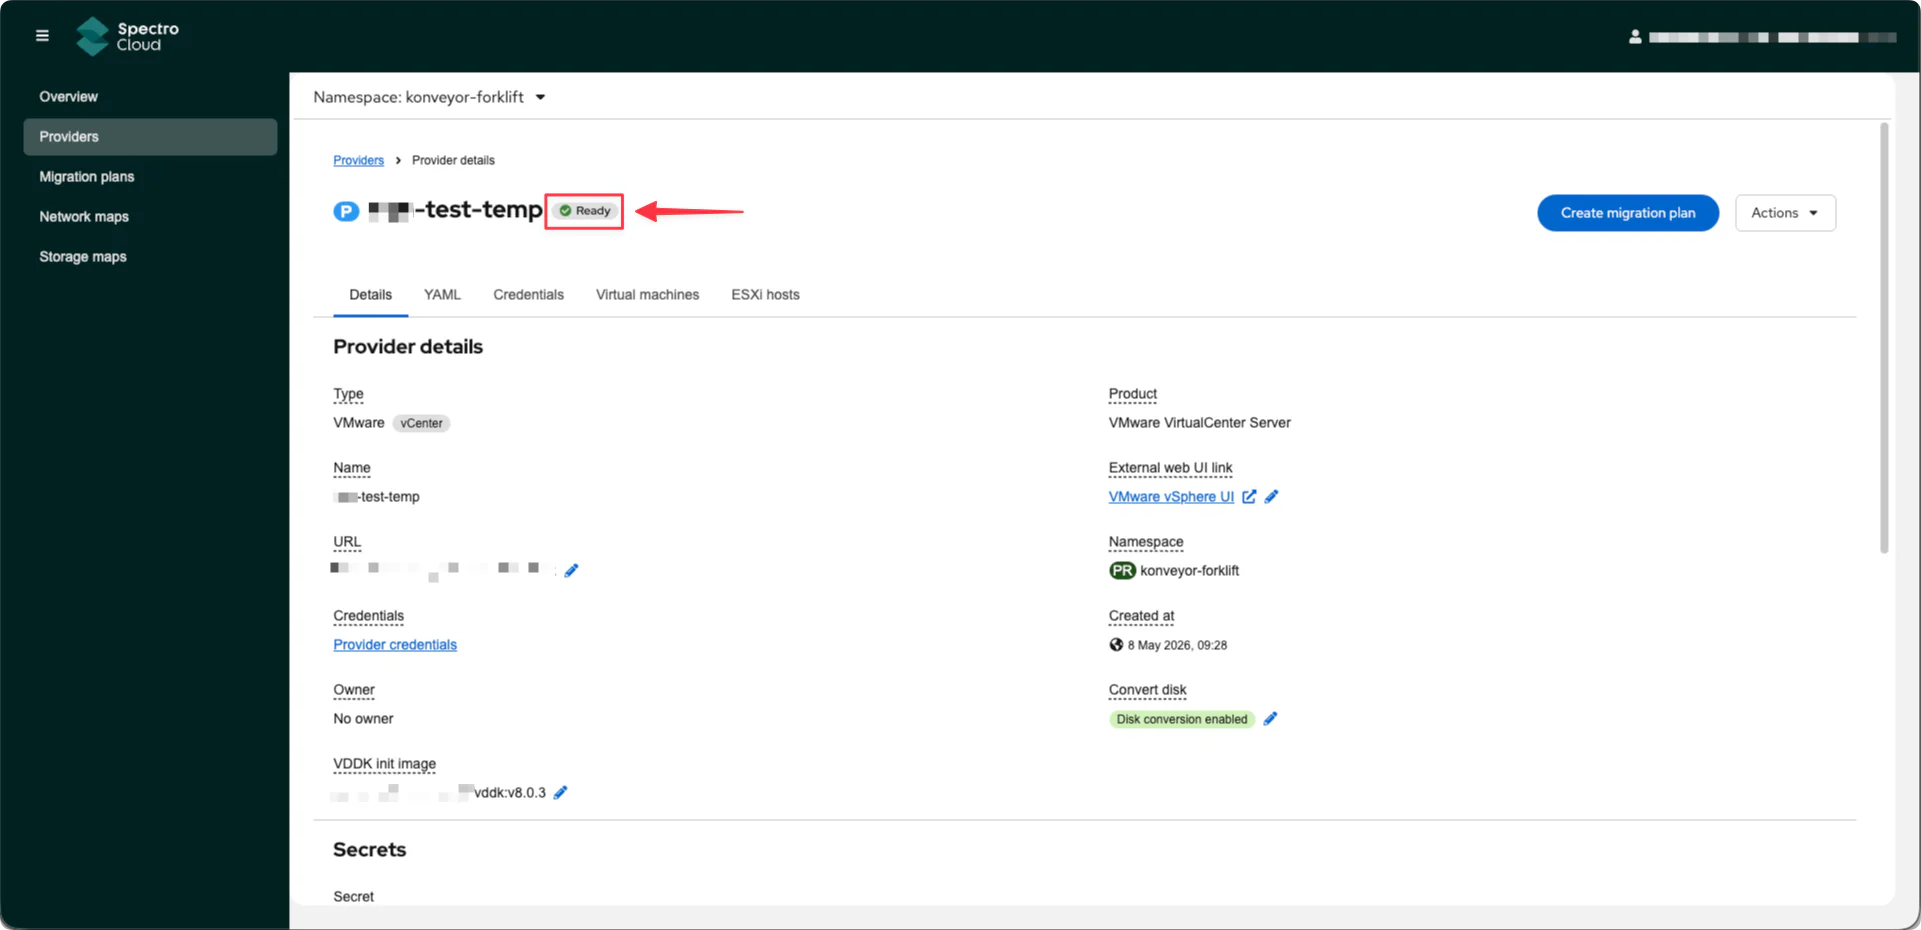
If the provider status is not Ready, check the Conditions section of the Details tab for any failed conditions.
Next Steps
-
You can now create migration plans in the VM Migration Assistant. Refer to the Create Migration Plans guide to start creating your plans.
-
If you want to explore additional provider settings, refer to Additional Configuration - Provider Settings for guidance.