Feature Flags
Feature flags allow system administrators to manage certain features available to the system's tenants. Use this capability to roll out new features to tenants in a controlled manner or prevent tenants from using Tech Preview features in production environments.
Features enabled by system administrators apply to all tenants in the system. Once a feature is enabled, it cannot be disabled for security and stability purposes. All feature flags are Tech Preview features. When a feature graduates from Tech Preview, the feature flag is removed, and the feature is automatically enabled for all tenants.
The following table lists all available feature flags and their supported platforms.
| Feature Flag | Description | Palette Support | Palette VerteX Support |
|---|---|---|---|
| AwsSecretPartition | Configure Amazon Web Services (AWS) Secret and AWS Top Secret cloud accounts and deploy Elastic Kubernetes Service (EKS) clusters in AWS Secret and Top Secret clouds. Palette VerteX also supports customizing endpoints for individual AWS services to meet the requirements of airgapped environments. Refer to our Add an AWS Account to Palette guide for more information. | ❌ | ✅ |
| AzureUSSecretCloud | Configure Azure Government Secret cloud accounts and deploy Azure IaaS clusters in Azure Government Secret cloud. Refer to our Register and Manage Azure Accounts guide for more information. | ❌ | ✅ |
| LxdMaas | Spawn multiple control plane nodes as LXD VMs and consolidate them on MAAS-managed servers while your worker nodes run on bare metal devices. Refer to our Create and Manage MAAS Clusters Using LXD VMs guide for more information. | ✅ | ✅ |
| HypershiftOpenshiftCluster | Deploy OpenShift clusters on MAAS using HyperShift host clusters. Refer to our Create and Manage MAAS OpenShift Clusters with HyperShift guide for more information. | ✅ | ❌ |
We recommend enabling features in test environment first, as certain features may have a significant impact on your production environment and current workloads.
Limitations
- All feature flags are disabled for multi-tenant SaaS. To enable a feature flag on a dedicated SaaS environment, contact your Spectro Cloud customer support representative.
Prerequisites
-
A self-hosted Palette or Palette VerteX instance.
-
A system administrator with the Operations Administrator or Root Administrator role.
-
Access to the system console.
Enable a Feature
-
Log in to the Palette VerteX system console.
-
From the left main menu, select Administration.
-
Select the Feature Flags tab.
-
Locate the feature you want to activate and toggle the switch to enable it. Once you enable the feature, you cannot disable it.
Customize AWS Secret and Top Secret Endpoints
With the AwsSecretPartition feature flag enabled, you can customize API endpoints for individual AWS services to meet the requirements of your airgapped environment. If your environment uses custom endpoints, you must configure them in the Palette VerteX system console before Palette VerteX can provision and manage clusters in AWS Secret or Top Secret cloud.
-
Log in to the Palette VerteX system console.
-
From the left main menu, select Administration.
-
Select the Feature Flags tab.
-
In the AwsSecretPartition section, select Configure Endpoints.
-
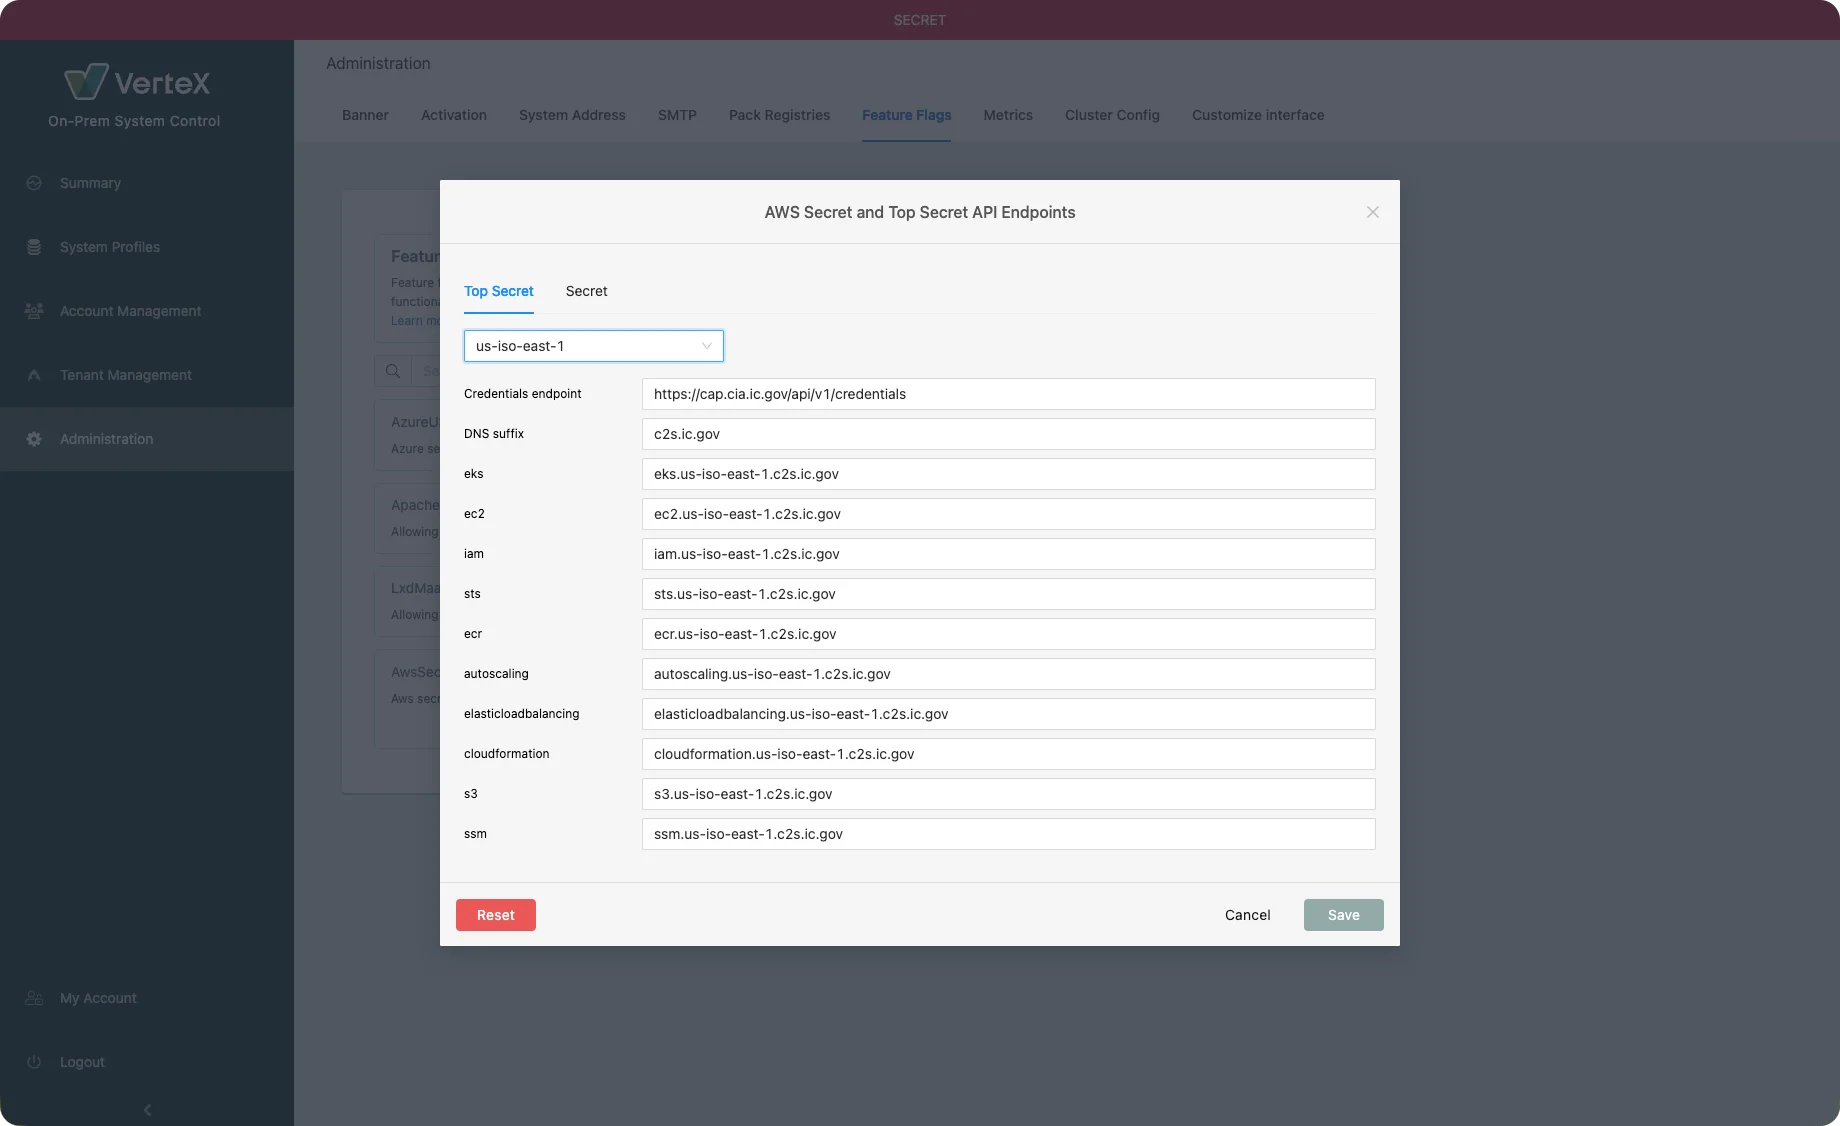
In the AWS Secret and Top Secret API Endpoints dialog, select the Secret or Top Secret tab depending on the partition you are configuring endpoints for.
-
Use the drop-down menu to select the applicable cloud region.
-
Use the following table to customize endpoints as needed. To discards any unsaved changes and restore all fields to their last saved configuration, select Reset.
Field Description Credentials endpoint The URL for the credentials provider used to obtain temporary security credentials. For AWS Top Secret (C2S) cloud, this is the C2S Access Portal (CAP). For AWS Secret (SC2S) cloud, this is the SC2S Access Portal (SCAP). DNS suffix The base domain suffix for AWS service endpoints in the selected region. eks Amazon Elastic Kubernetes Service ec2 Amazon Elastic Compute Cloud iam AWS Identity and Access Management sts AWS Security Token Service ecr Amazon Elastic Container Registry autoscaling AWS Auto Scaling elasticloadbalancing Elastic Load Balancing cloudformation AWS CloudFormation s3 Amazon Simple Storage Service ssm AWS Systems Manager -
Ensure your endpoint values are correct and Save your changes.
Incorrect endpoints can prevent Palette VerteX from communicating with AWS services, which may cause cluster provisioning or management operations to fail.
You can update endpoints at any time, including after workload clusters are deployed. When you update an endpoint, Palette VerteX restarts the internal cluster management controller pods to apply the new endpoint configurations. Updated endpoint configurations are applied to existing clusters during the next reconciliation cycle, which occurs approximately every 15 minutes. Workloads on running clusters are not interrupted during this process.
Validate
Validation steps vary based on the feature enabled. In general, if you do not activate a feature, you cannot view any options related to the feature.
For example, if you enable the AwsSecretPartition feature flag in Palette VerteX, the option AWS US Secret is available from the Partition drop-down menu at Tenant Settings > Cloud Accounts > Add AWS Account, and you can select your AWS Secret cloud account when deploying an EKS cluster. Likewise, if you do not enable the AwsSecretPartition feature flag, you do not have the option to register an AWS Secret cloud account and cannot deploy clusters to AWS Secret cloud.