Create and Manage AWS EKS Cluster
Palette supports creating and managing Amazon Web Services (AWS) Elastic Kubernetes Service (EKS) clusters deployed to an AWS account. This section guides you on how to create an EKS cluster in AWS that Palette manages.
EKS-optimized Amazon Linux 2 (AL2) AMIs are disabled in Palette. This means:
- For new clusters, you cannot select AL2 AMIs for EKS worker nodes in Palette.
- For existing clusters, you must create new worker nodes using AL2023 AMIs. Existing AL2 AMI worker nodes will no
longer receive bug fixes or security patches.
- In addition, Kubernetes upgrades to v1.33 and later are not supported on EKS clusters with AL2 worker nodes. If you want to upgrade your cluster to v1.33 or later, you must first migrate your workloads to AL2023 worker nodes.
Refer to our Scenario - Unable to Upgrade EKS Worker Nodes from AL2 to AL2023 guide for help with migrating workloads.
Limitations
-
You must use Palette VerteX to deploy EKS clusters in AWS Secret or Top Secret cloud. Multi-tenant Palette SaaS, dedicated Palette SaaS, and self-hosted Palette instances are not supported.
-
Day-2 node pool operations cannot be performed on EKS clusters deployed prior to Palette version 4.7.3 that have both Enable Nodepool Customization enabled and Amazon Linux 2023 (AL2023) node labels. You must create a new node pool with the desired Amazon Machine Image (AMI) and node pool customizations and migrate existing workloads to the new node pool. For an example of how to migrate workloads, refer to the AWS Scale, Upgrade, and Secure Clusters guide.
Prerequisites
-
Access to an AWS cloud account.
-
Palette integration with AWS account. Review Add AWS Account for guidance.
-
If you are using EKS Pod Identity to authenticate Palette with your AWS account, you must configure the
iamAuthenticatorConfig.mapUserssection of the Kubernetes layer of your AWS EKS cluster profiles with at least one user entry. This configuration is required for the EKS Pod Identity feature to operate correctly. It grants users access to the kubeconfig file of EKS workload clusters and allows the Palette management cluster to access the workload cluster.warningIf you do not configure
iamAuthenticatorConfigwith a user entry, neither your users nor the Palette management cluster can access the EKS cluster. As a result, the cluster becomes stuck during deletion, and its pod identity associations are not cleaned up.As per the following example, these users must be added to the
system:mastersgroup to have admin access to the cluster. Replace<aws-account-id>,<username>, and<k8s-username>with your AWS account ID, the IAM username, and the desired Kubernetes username, respectively. Add additional users as needed.Configuration templateiamAuthenticatorConfig:
mapUsers:
- userarn: arn:aws:iam::<aws-account-id>:user/<username>
username: <k8s-username>
groups:
- system:masters
-
-
An infrastructure cluster profile for AWS EKS. When you create the profile, ensure you choose EKS as the Managed Kubernetes cloud type. Review Create an Infrastructure Profile for guidance.
infoFor guidance on all available configuration options for the EKS Kubernetes pack, review the Additional Details for the pack.
-
If you choose to assign an Amazon Linux 2023 AMI (AL2023) to your worker nodes and you are using PersistentVolumes (PVs) or PersistentVolumeClaims (PVCs), you must make additional edits to your AWS EKS cluster profile to configure IAM Roles for Service Accounts (IRSA) for the Amazon Elastic Block Store (EBS) Container Storage Interface (CSI).
Configure IRSA for Amazon EBS CSI
Use the following steps to configure IRSA for the Amazon EBS CSI. For instances launched on Amazon Linux 2023, AWS Instance Metadata Service version 2 (IMDSv2) is enforced by default, and IRSA is the recommended approach for providing IAM permissions to Amazon EBS CSI.
-
Log in to Palette.
-
Ensure you are in the correct project scope.
-
From the left main menu, navigate to the Profiles page.
-
Select an existing AWS EKS cluster profile or create a new AWS EKS cluster profile that meets your requirements, including any necessary add-on packs or additional Helm charts.
-
Select the Kubernetes layer of your cluster profile.
-
Use the YAML editor to configure IRSA roles for the
managedControlPlaneandmanagedMachinePool.Example configurationmanagedControlPlane:
---
irsaRoles:
- name: "{{.spectro.system.cluster.name}}-irsa-cni"
policies:
- arn:aws:iam::aws:policy/AmazonEKS_CNI_Policy
serviceAccount:
name: aws-node
namespace: kube-system
- name: "{{.spectro.system.cluster.name}}-irsa-csi"
policies:
- arn:aws:iam::aws:policy/service-role/AmazonEBSCSIDriverPolicy
---
managedMachinePool:
roleAdditionalPolicies:
- "arn:aws:iam::aws:policy/service-role/AmazonEBSCSIDriverPolicy" -
Click Confirm Updates after editing.
-
Select the Storage layer of your cluster profile.
-
Use the YAML editor to add an IAM role ARN annotation to the AWS EBS CSI Driver so that the IRSA role is correctly referenced. Replace
<aws-account-id>with your AWS account ID.Example configurationcharts:
...
aws-ebs-csi-driver:
...
controller:
...
serviceAccount:
# A service account will be created for you if set to true. Set to false if you want to use your own.
create: true
name: ebs-csi-controller-sa
annotations: {
"eks.amazonaws.com/role-arn":"arn:aws:iam::<aws-account-id>:role/{{.spectro.system.cluster.name}}-irsa-csi"
}
## Enable if EKS IAM for SA is used
# eks.amazonaws.com/role-arn: arn:<partition>:iam::<account>:role/ebs-csi-role
automountServiceAccountToken: true -
Click Confirm Updates after editing.
-
Click Save Changes on the cluster profile page.
-
Once the cluster is running and healthy, verify that the PV or PVC status is
Boundby issuing one of the followingkubectlcommands.Example command for PVskubectl get pv --output wideExample output for PVsNAME CAPACITY ACCESS MODES RECLAIM POLICY STATUS CLAIM STORAGECLASS VOLUMEATTRIBUTESCLASS AGE VOLUMEMODE
pv-xyz... 10Gi RWO Delete Bound wordpress/data-wordpress-wordpress-mariadb-0 spectro-storage-class <unset> 16m Filesystem
pv-abc... 8Gi RWO Delete Bound wordpress/wordpress-wordpress spectro-storage-class <unset> 16m FilesystemExample command for PVCskubectl get pvc --all-namespaces --output wideExample output for PVCsNAMESPACE NAME STATUS VOLUME CAPACITY ACCESS MODES STORAGECLASS VOLUMEATTRIBUTESCLASS AGE VOLUMEMODE
wordpress data-wordpress-wordpress-mariadb-0 Bound pvc-xyz... 10Gi RWO spectro-storage-class <unset> 16m Filesystem
wordpress wordpress-wordpress Bound pvc-abc... 8Gi RWO spectro-storage-class <unset> 16m Filesystem
-
-
The EC2 instance hop limit must be increased to 2 to allow IMDSv2 responses to traverse the additional network namespace hop introduced by containerized workloads.
Palette deploys EKS clusters using AL2023 AMIs by default, which enforce IMDSv2. IMDSv2 has a default hop limit of 1, and this means containers running in non-host networking mode cannot reach the IMDSv2 service. This causes failures in the AWS CSI driver and any pod that accesses AWS resources via IMDSv2.
A hop limit of 2 is also required by other EKS components, including the AWS Load Balancer Controller, which relies on IMDS for metadata introspection.
We recommend applying this setting at the account level for each region you intend to deploy into. Account-level changes only apply to newly launched instances, therefore, existing instances must be updated individually. Refer to the AWS documentation for guidance on configuring the hop limit for new instances and existing instances.
-
Deploying EKS clusters with the Cilium pack requires using the Replace Kube-Proxy With EBPF preset and configuring additional values in the Cilium layer of your cluster profile. The required configuration varies based on whether the cluster is deployed with dynamic or static placement. Expand the following panel for the required configuration.
Cilium Replace Kube-Proxy With EBPF configuration
- Dynamic
- Static
Parameter Required Value Description charts.cilium.endpointRoutes.enabledtrueEnables per-endpoint routing to allow direct pod-to-pod communication in elastic network interface (ENI) mode without encapsulation. charts.cilium.eni.enabledtrueEnables AWS ENI integration for direct networking instead of using an overlay network. charts.cilium.ipam.mode"eni"Uses AWS ENI-based Internet Protocol address management (IPAM) to allocate pod IPs directly from AWS Virtual Private Cloud (VPC) subnets. charts.cilium.k8sServiceHost#k8sServiceHost: "auto"Specifies the Kubernetes API server host address. This field must be disabled in lieu of charts.cilium.k8sServiceHostRef, which points to Palette's managed ConfigMap.charts.cilium.k8sServiceHostRef.keyk8s-service-hostSpecifies the key within Palette's managed k8s-service-hostConfigMap, which contains the Kubernetes API server endpoint.charts.cilium.k8sServiceHostRef.namepalette-cilium-configSpecifies the name of Palette's managed ConfigMap, which contains the Kubernetes API server endpoint. charts.cilium.k8sServicePort"443"Specifies the Kubernetes API server port. Required when using k8sServiceHostReffor EKS clusters.charts.cilium.kubeProxyReplacement"true"Enables eBPF-based kube-proxy replacement because kube-proxy is disabled, and Cilium must handle service load balancing. charts.cilium.kubeProxyReplacementHealthzBindAddr0.0.0.0:10256Binds the health check service to 0.0.0.0:10256for the kube-proxy replacement.charts.cilium.autoDirectNodeRoutesfalseDisables automatic direct routing between nodes because AWS ENI mode already manages routing, making additional direct routes unnecessary. charts.cilium.routingMode"native"Uses native routing mode because AWS ENI mode supports direct pod-to-pod routing, making encapsulation unnecessary. Parameter Required Value Description charts.cilium.bpf.masqueradetrueEnables eBPF masquerading because AWS handles network address translation (NAT) and Internet Protocol (IP) address masquerading through the elastic network interface (ENI). charts.cilium.enableIPv4MasqueradetrueEnables Internet Protocol version 4 (IPv4) masquerading for outgoing packets because AWS ENI mode provides direct pod-to-pod routing without NAT. charts.cilium.endpointRoutes.enabledtrueEnables per-endpoint routing to allow direct pod-to-pod communication in ENI mode without encapsulation. charts.cilium.eni.enabledtrueEnables AWS ENI integration for direct networking instead of using an overlay network. charts.cilium.ipam.mode"eni"Uses AWS ENI-based IP address management (IPAM) to allocate pod IPs directly from AWS Virtual Private Cloud (VPC) subnets. charts.cilium.k8sServiceHost#k8sServiceHost: "auto"Specifies the Kubernetes API server host address. This field must be disabled in lieu of charts.cilium.k8sServiceHostRef, which points to Palette's managed ConfigMap.charts.cilium.k8sServiceHostRef.keyk8s-service-hostSpecifies the key within Palette's managed k8s-service-hostConfigMap, which contains the Kubernetes API server endpoint.charts.cilium.k8sServiceHostRef.namepalette-cilium-configSpecifies the name of Palette's managed ConfigMap, which contains the Kubernetes API server endpoint. charts.cilium.k8sServicePort"443"Specifies the Kubernetes API server port. Required when using k8sServiceHostReffor EKS clusters.charts.cilium.kubeProxyReplacement"true"Enables eBPF-based kube-proxy replacement because kube-proxy is disabled, and Cilium must handle service load balancing. charts.cilium.kubeProxyReplacementHealthzBindAddr0.0.0.0:10256Binds the health check service to 0.0.0.0:10256for the kube-proxy replacement.charts.cilium.autoDirectNodeRoutesfalseDisables automatic direct routing between nodes because AWS ENI mode already manages routing, making additional direct routes unnecessary. charts.cilium.routingMode"native"Uses native routing mode because AWS ENI mode supports direct pod-to-pod routing, making encapsulation unnecessary.
-
If you need to override the default service Classless Inter-Domain Routing (CIDR), configure the service ClusterIP range in the Kubernetes (EKS) pack. Additionally, if you want to use your own VPC and subnets, configure the pod CIDR in the AWS VPC CNI (Helm) pack.
Pods running on the control plane continue to receive IP addresses from the node CIDR range. The custom pod CIDR applies only to pods scheduled on worker nodes.
-
An EC2 key pair for the target region that provides a secure connection to your EC2 instances. A key pair is required for dynamic placement and is optional for static placement. To learn how to create a key pair, refer to the Amazon EC2 key pairs resource.
infoDynamic placement means Palette automatically creates and manages a new VPC and subnets for your EKS cluster. Static placement means Palette uses your existing VPC, requiring you to specify the necessary network resources.
-
Your Amazon EKS cluster must be deployed with at least one worker node to host the Palette agent, which is necessary for Palette to manage the cluster. Because of EKS architecture constraints, the agent cannot be installed on the control plane.
- The minimum instance type required is t3.xlarge with at least 20 GB of storage.
- Be sure at least one worker node is always available so Palette can continue managing the cluster.
-
To access your EKS cluster using kubectl, you will need the aws-iam-authenticator plugin installed. If you are using a custom OIDC provider, you will need the kubelogin plugin installed. Refer to the Access EKS Cluster section for more information.
-
To use secrets encryption, which is available only during EKS cluster creation, you must have created an AWS Key Management Service (KMS) key. If you do not have one, review Enable Secrets Encryption for EKS Cluster for guidance.
-
To use disk encryption, you must have created an AWS KMS key and set the appropriate configuration in the Kubernetes layer of your cluster profile. Review Enable Disk Encryption for EKS Cluster for guidance.
-
If you are deploying your cluster in AWS Secret or Top Secret cloud, you must configure Image Swap in the Kubernetes layer of your cluster profile to redirect public image requests to your internal or Elastic Container Registry.
warningFor static network deployments, you must have port 6443 open between Palette and the workload cluster. Refer to the Network Ports documentation for detailed network architecture diagrams and to learn more about the ports used for communication.
-
If you do not provide your own VPC, Palette creates one for you with compute, network, and storage resources in AWS when it provisions Kubernetes clusters. Ensure there is sufficient capacity in the preferred AWS region to create the following resources. Note that Palette does not create these resources if you specify an existing VPC.
- Virtual CPU (vCPU)
- VPC
- Elastic IP
- Internet Gateway
- Elastic Load Balancers
- Network Address Translation (NAT) Gateway
infoTo enable automated subnet discovery to create external load balancers, you need to add tags to the VPC public subnets. For more information about tagging VPC networks, refer to the AWS EKS VPC Subnet Discovery reference guide. Use the AWS Tag Editor and specify the region and resource type. Then, add the following tags. Replace the value
yourClusterNamewith your cluster's name. To learn more about the Tag Editor, refer to the AWS Tag Editor reference guide.kubernetes.io/role/elb = 1sigs.k8s.io/cluster-api-provider-aws/role = publickubernetes.io/cluster/[yourClusterName] = sharedsigs.k8s.io/cluster-api-provider-aws/cluster/[yourClusterName] = owned
Deploy an AWS EKS Cluster
-
Log in to Palette.
-
Ensure you are in the correct project scope.
-
From the left main menu, select Clusters and click Add New Cluster.
-
In Public Clouds, under Managed Kubernetes, select AWS EKS.
-
In the bottom-right corner, click Start AWS EKS Configuration.
-
Fill out the following basic information and click Next.
Field Description Cluster Name A custom name for the cluster. Description Use the description to provide context about the cluster. Tags Assign any desired cluster tags. Tags on a cluster are propagated to the Virtual Machines (VMs) deployed to the target environments. Example: region:us-east-1aorzone:vpc-private-us-east-1a.Cloud Account If you already added your AWS account in Palette, select it from the drop-down Menu. Otherwise, click Add New Account and add your AWS account information. To learn how to add an AWS account, review the Add an AWS Account to Palette guide.
-
Choose between deploying your cluster using individual cluster profiles or a single cluster template.
- Cluster Profiles
- Cluster Templates
-
In the Cluster setup type window, choose Cluster Profiles > Add Cluster Profile.
-
Select the appropriate full or infrastructure cluster profile and Confirm your selection.
-
Review the layers of your cluster profile. Use the drop-down menus to select the appropriate cluster profile version, add necessary add-on profiles, and make changes to YAML configuration files as needed. When finished, select Next.
info- Cluster profile versions linked to cluster templates cannot be used in the cluster profile workflow.
- For ease of reuse and to persist changes across clusters using the same cluster profile, we recommend creating a new version of your cluster profile rather than making inline changes.
-
In the Cluster setup type window, choose Cluster Template > Select Cluster Template.
-
Select the appropriate cluster template and Confirm your selection.
-
Expand the Maintenance policy and Linked profiles panels to review the configuration of your cluster template.
If you need to make any changes, such as swapping your maintenance policy or updating your cluster profile version, you must exit the cluster deployment workflow and modify your cluster template before proceeding. If no changes are needed, select Next.
-
Review the layers of your cluster profile. If no changes are needed, select Next.
warningCluster profile changes, such as modifying your cluster profile version, adding additional add-on profiles, and editing YAML configuration files, are not allowed when deploying a cluster. Once a cluster profile is linked to a cluster template, that version of the cluster profile is locked to prevent configuration drift across clusters. If you need to make changes, you must create a new version of your cluster profile and modify your cluster template to use the new version.
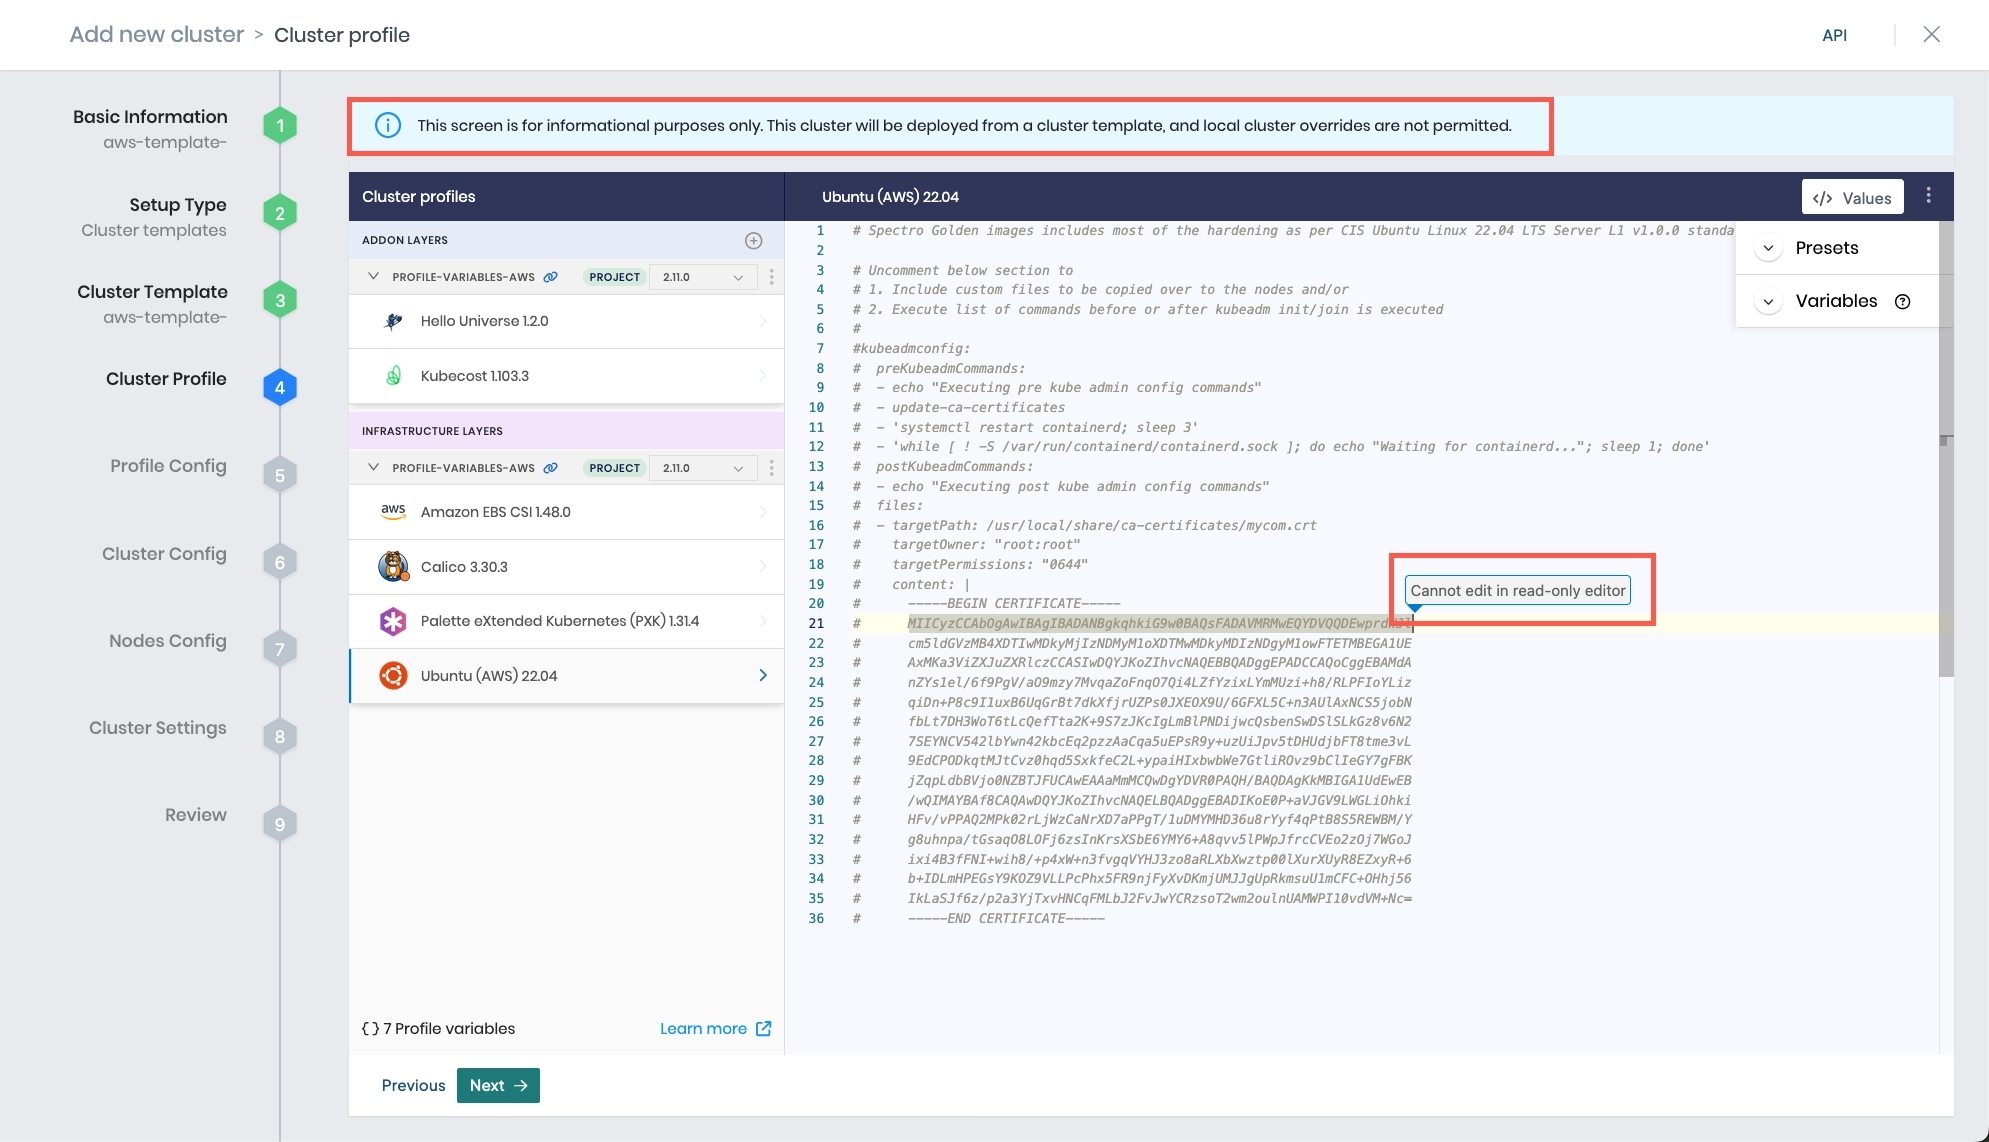
- You can configure custom OpenID Connect (OIDC) for EKS clusters at the Kubernetes layer. Refer to the Access EKS Cluster section for additional guidance.
-
The Profile variables configuration window opens if your cluster profile is configured to use cluster profile variables. Fill in the appropriate values, and select Next.
-
Provide the following cluster configuration information and click Next to continue.
Parameter Description Region Use the drop-down menu to choose the AWS region where you would like to provision the cluster. SSH Key Pair Name Choose the SSH key pair for the region you selected. This is required for dynamic placement and optional for static placement. SSH key pairs must be pre-configured in your AWS environment. This is called an EC2 Key Pair in AWS. The key you select is inserted into the provisioned VMs. Enable static placement (Optional) By default, Palette uses dynamic placement. This creates a new VPC for the cluster that contains two subnets in different Availability Zones (AZs), which is required for EKS cluster deployment. Palette places resources in these clusters, manages the resources, and deletes them when the corresponding cluster is deleted.
If you want to place resources into pre-existing VPCs, toggle the Enable static placement (Optional) option, and provide the VPC ID in the Virtual Private Cloud (VPC) ID field that displays with this option enabled.
Static placement is required for EKS clusters deployed in AWS Secret or Top Secret cloud.Cluster Endpoint Access This setting provides access to the Kubernetes API endpoint. Select Private, Public, or Private & Public. If you are deploying your cluster in AWS Secret or Top Secret cloud, use Private & Public.
For fully private endpoint access, deploy a self-hosted Private Cloud Gateway (PCG) with network access to the cluster and provision the cluster through it. If you select Private without a PCG, Palette initially creates the cluster in Private & Public mode and changes it to Private after cluster provisioning completes.
For more information, refer to the Amazon EKS cluster endpoint access control reference guide.Public Access CIDRs This setting controls which IP address CIDR ranges can access the cluster. To fully allow unrestricted network access, enter 0.0.0.0/0in the field. For more information, refer to the Amazon EKS cluster endpoint access control reference guide.
You can update this setting after deployment. Refer to Update Endpoint Access CIDRs.Private Access CIDRs This setting controls which private IP address CIDR ranges can access the cluster. Private CIDRs provide a way to specify private, self-hosted, and air-gapped networks or Private Cloud Gateway (PCG) that may be located in other VPCs connected to the VPC hosting the cluster endpoint.
To restrict network access, replace the pre-populated0.0.0.0/0with the IP address CIDR range that should be allowed access to the cluster endpoint. Only the IP addresses that are within the specified VPC CIDR range - and any other connected VPCs - will be able to reach the private endpoint. For example, while using0.0.0.0/0would allow traffic throughout the VPC and all peered VPCs, specifying the VPC CIDR10.0.0.0/16would limit traffic to an individual VPC. For more information, refer to the Amazon EKS cluster endpoint access control reference guide.
You can update this setting after deployment. Refer to Update Endpoint Access CIDRs.Enable key encryption (Optional) Use this option for secrets encryption. You must have an existing AWS Key Management Service (KMS) key you can use. Toggle the Enable key encryption (Optional) option and use the Provider Amazon Resource Name (ARN) drop-down menu to select the KMS key ARN.
If you do not have a KMS key and want to create one, review Enable Secrets Encryption for EKS Cluster. Once your KMS key is created, return to this step to enable secrets encryption with your new KMS key ARN.Override Cluster API cluster configuration Enable if you want to provide custom Cluster API manifests in YAML format. This is an advanced option that allows you to customize the underlying CAPI objects used to provision and manage your cluster. When enabled, the Update Cluster API cluster configuration option becomes available. Click this button to view the YAML code editor drawer, where you can provide your override configuration. Review the Override CAPI Properties documentation to learn more about this feature. Update worker pools in parallel Use this option to efficiently manage workloads by updating multiple worker pools simultaneously. warningIf you set the cluster endpoint to Public, ensure you specify
0.0.0.0/0in the Public Access CIDR field to open it to all possible IP addresses. Otherwise, Palette will not open it up entirely. We recommend specifying the Private & Public option to cover all the possibilities. -
Provide the following node pool and cloud configuration information. If you will be using Fargate profiles, you can add them here.
infoTo automatically scale the number of worker nodes for EKS clusters, you must add the AWS Cluster Autoscaler pack to your cluster profile.
Node Configuration Settings
Parameter Description Node pool name A descriptive name for the node pool. Number of nodes in the pool The number of nodes in the worker pool. Additional Labels (Optional) Optional labels to nodes in key-value format. For general information about applying labels, review the Node Labels guide. Example: "environment": "production".Additional Annotations (Optional) Additional Kubernetes annotations to assign to each worker node. Override Cluster API node pool configuration (Optional) Enable if you want to provide custom Cluster API manifests in YAML format. This is an advanced option that allows you to customize the underlying CAPI objects used to provision and manage your node pool. When enabled, the Update Cluster API node pool configuration option becomes available. Click this button to view the YAML code editor drawer, where you can provide your override configuration. Review the Override CAPI Properties documentation to learn more about this feature. Taints (Optional) You can apply optional taint labels to a node pool during cluster creation or edit taint labels on an existing cluster. Review the Node Pool management page and Taints and Tolerations guide to learn more. Toggle the Taint button to create a taint label. When tainting is enabled, you need to provide a custom key-value pair. Use the drop-down menu to choose one of the following Effect options:
- NoSchedule - Pods are not scheduled onto nodes with this taint.
- PreferNoSchedule - Kubernetes attempts to avoid scheduling pods onto nodes with this taint, but scheduling is not prohibited.
- NoExecute - New pods that do not tolerate the taint will not be scheduled on the node, and existing pods on the node, if any, will be evicted if they do not tolerate the taint.Dedicate node pool for system pods Enable if you want the node pool to run system pods only. For more information, refer to Dedicated node pool for system pods. Cloud Configuration Settings
Parameter Description Instance Option Choose a pricing method:
- On-Demand - Provides stable and uninterrupted compute capacity at a higher cost.
- Spot - Allows you to bid for unused EC2 capacity at a lower cost.
We recommend you base your choice on your application's requirements.Instance Type Select the instance type to use for all nodes in the node pool. Amazon Machine Image (AMI) Type Specify a base AMI to use for your worker nodes:
- AL2023_x86_64_STANDARD (default)
- AL2023_x86_64_NEURON
- AL2023_x86_64_NVIDIA
The AMI type cannot be modified post-deployment. Refer to the Node Customization section of the Kubernetes EKS pack for configurable options available for these AMIs.
If using an Amazon Linux 2023 (AL2023) AMI and using an AWS CSI pack such as Amazon EBS CSI, Amazon EFS CSI, or Amazon Cloud Native, you must configure IAM Roles for Service Accounts (IRSA). IRSA is also required if using the AWS Application Loadbalancer. Refer to the Scenario - PV/PVC Stuck in Pending Status for EKS Cluster Using AL2023 AMI troubleshooting guide for further information.Enable Nodepool Customization (Optional) Activate additional node pool customization options:
- Amazon Machine Image (AMI) ID (Optional) - Use a pre-configured VM image by providing the ID value of the AMI. The AMI ID can be updated post-deployment, but the base AMI type must always match the type specified in the Amazon Machine Image (AMI) Type field, and the AMI must be compatible with the Kubernetes version specified in the cluster profile.
CAUTION: If you do not specify an AMI ID, Palette will use the Amazon EKS AMI for the node pool. As such, any future updates to the underlying Amazon EKS AMI in Palette will trigger cluster repaves. To avoid unexpected repaves, explicitly set the AMI ID. Refer to the AWS documentation for the latest AMI IDs.
- Disk Type (Optional) - Specify the disk type to use.Root Disk size (GB) Choose a disk size based on your requirements. The default size is 60.Fargate Profiles
You can create one or more Fargate profiles for the EKS cluster to use. Click + Add Fargate Profile. For more information about Fargate profiles, refer to the AWS Fargate reference guide.
Parameter Description Name A custom name for the Fargate profile. Subnets Pods running on Fargate Profiles are not assigned public IP addresses, so only private subnets (with no direct route to an Internet Gateway) are accepted for this parameter. For dynamic provisioning, this input is not required and subnets are automatically selected. Selectors Define a pod selector by providing a target namespace and optional labels. Pods with a matching namespace and app labels are scheduled to run on dynamically provisioned compute nodes.
You can have up to five selectors in a Fargate profile, and a pod only needs to match one selector to run using the Fargate profile.infoYou can add new worker pools if you need to customize certain worker nodes to run specialized workloads. As an example, the default worker pool may be configured with the m3.large instance types for general-purpose workloads, and another worker pool with instance type g2.2xlarge can be configured to run GPU workloads.
-
Click Next to continue.
-
On the Cluster Settings page, configure additional options as needed. If you are deploying your cluster using cluster templates, a Cluster Timezone is required.
Left Menu Item Additional Information Cluster Timezone Specify the time zone where your cluster is being deployed. The time zone is used in maintenance policies to determine when updates are rolled out to clusters deployed with cluster templates. Manage machines Set an OS patching schedule and specify nodes behavior when creating your cluster, including upgrading your nodes to use the latest OS patch version and allowing reboots. Schedule scans Enable any scan options you want Palette to perform and select a scan schedule. Palette supports Kubernetes configuration security, penetration testing, and conformance testing. Refer to Compliance Scan for details on each scan type. Schedule backups Schedule backups for your entire cluster or etcd. Refer to Backup and Restore for more information. RBAC Map a set of users or groups to a Kubernetes Role-Based Access Control (RBAC) role. This is required when custom OpenID Connect (OIDC) is configured. Refer to the following guides for more information:
- Create Role Bindings
- Palette eXtended Kubernetes (PXK)Location Specify the location of your cluster by entering the address in the search bar and selecting one of the options in the drop-down. For example, London, Greater London, England, United Kingdom. This is used for display purposes and does not impact cluster functionality. -
Select Validate to review your cluster configurations and settings.
-
If no changes are needed, select Finish Configuration to deploy your cluster.
To monitor the status of your cluster deployment, from the left main menu, select Clusters and choose your cluster. The cluster Overview tab displays the status and health of your cluster, as well as deployment details. Use the Events tab to monitor the deployment in real time. Provisioning may take several minutes.
For information on how to access your cluster using the kubectl CLI, review Access EKS Cluster.
Validate
You can validate your cluster is up and in Running state.
-
Log in to Palette.
-
Navigate to the left main menu and select Clusters. The Clusters page displays a list of all available clusters that Palette manages.
-
Click on the cluster you created to view its details page.
-
Ensure the Cluster Status field displays Running.
Access EKS Cluster
You can access your EKS cluster using the kubectl CLI with a kubeconfig file. Authentication is required, and the availability of the kubeconfig file through Palette depends on your chosen authentication method, as shown in the following table.
| Authentication Method | Kubeconfig Availability |
|---|---|
| AWS IAM Authenticator Plugin | ✅ |
| Default AWS Authentication | ❌ |
| Custom OIDC | ✅ |
Based on your chosen authentication method, follow the instructions in the appropriate tab to access your Amazon EKS cluster through kubectl.
- AWS IAM Authenticator Plugin
- Default AWS Authentication
- Custom OIDC
To access an Amazon EKS cluster using the AWS IAM Authenticator plugin, follow these steps:
-
Configure your AWS CLI credentials. Refer to Configuration and Credential File Settings for guidance.
-
Download and install the AWS IAM Authenticator plugin for your system. Refer to Installing the AWS IAM Authenticator for guidance.
Example steps to install
-
Download the binary from the GitHub releases page.
-
Move the binary to a directory included in your system's
PATHand rename it toaws-iam-authenticator.Example commandsudo mv Downloads/aws-iam-authenticator_0.7.9_darwin_arm64 /usr/local/bin/aws-iam-authenticator -
Make the binary executable.
sudo chmod +x /usr/local/bin/aws-iam-authenticator -
Verify the installation:
aws-iam-authenticator --versionExample output{"Version":"0.7.9","Commit":"19000d354fa0828012e45dc52039c73177f7cde8"}
-
-
Download the kubeconfig file for the Amazon EKS cluster from Palette. Refer to Kubeconfig for guidance.
Once you have downloaded your kubeconfig, you can use kubectl to access your cluster and apply manifests.
To access an Amazon EKS cluster using the AWS CLI's built-in authentication, follow these steps:
-
Configure your AWS CLI credentials. Refer to Configuration and Credential File Settings for guidance.
-
Ensure you have the following IAM permissions to download the kubeconfig and access the Amazon EKS cluster. Refer to Amazon EKS identity-based policy examples for guidance.
eks:DescribeClustereks:AccessKubernetesApi
-
Download the kubeconfig file from the Amazon EKS cluster using the AWS CLI. Refer to Connect kubectl to an EKS cluster for guidance.
Example commandaws eks update-kubeconfig --region <region> --name <cluster-name>
Once you have downloaded your kubeconfig, you can use kubectl to access your cluster and apply manifests.
To access an Amazon EKS cluster using a custom OIDC provider, follow these steps:
-
Ensure your Amazon EKS cluster has an associated OIDC provider by configuring it in the Kubernetes layer. Refer to the Kubernetes (EKS) pack documentation for guidance.
- If you have not yet associated an OIDC provider with your cluster, use kubelogin. We recommend kubelogin due to its ease of authentication.
-
Ensure your OIDC user or group is mapped to an
adminorclusteradminKubernetes RBAC Role or ClusterRole. To learn how to map a Kubernetes role to users and groups, refer to Create Role Bindings. -
Download the kubeconfig file for the Amazon EKS cluster from Palette. Refer to Kubeconfig for guidance.
Once you have downloaded your kubeconfig and configured it to use your OIDC provider, you can use kubectl to access your cluster and apply manifests.
For guidance in setting up kubectl, review the Kubectl guide.
Update Endpoint Access CIDRs
After you deploy an EKS cluster, you can add, remove, or replace the CIDR ranges in Public Access CIDRs and Private Access CIDRs. Palette applies the change to the EKS cluster endpoint within a few minutes and does not repave the worker nodes.
Palette displays only the CIDR fields that match the Cluster Endpoint Access setting of the cluster. For example, if you deployed the cluster with Public endpoint access, only Public Access CIDRs is available. You cannot change Cluster Endpoint Access after deployment.
Keep the following rules in mind when you update the CIDR ranges:
-
Each field must contain at least one CIDR range. To allow access from any IP address, use
0.0.0.0/0. -
In Public Access CIDRs, use publicly routable CIDR ranges. Amazon EKS rejects reserved ranges, such as the documentation range
203.0.113.0/24, and Palette does not display the error that EKS returns.
Use the following steps to update the endpoint access CIDRs.
-
Log in to Palette.
-
From the left main menu, select Clusters, and then select your EKS cluster.
-
From the cluster details page, select Settings > Cluster Settings.
-
Select Cluster Configuration.
-
In Public Access CIDRs or Private Access CIDRs, add the CIDR ranges that need access and remove the ranges that no longer need access. To replace a range, remove it and add the new range.
-
Select Save Changes.
Validate the CIDR Update
The following steps use the AWS CLI to confirm a change to Public Access CIDRs. Configure your AWS CLI credentials
for the AWS account that hosts the cluster. The credentials need the eks:DescribeCluster permission. Refer to
Configuration and Credential File Settings
for guidance.
-
Wait a few minutes for Palette to apply the change to the EKS cluster endpoint.
-
Use the AWS CLI to list the public access CIDR ranges of the EKS cluster.
aws eks describe-cluster --name <eks-cluster-name> --region <region> --query "cluster.resourcesVpcConfig.publicAccessCidrs" --output jsonReplace
<eks-cluster-name>with the name of the cluster in the Amazon EKS console and<region>with the AWS region of the cluster. -
Verify that the output lists the CIDR ranges that you saved in Palette. Amazon EKS might list the ranges in a different order.
Example Output[
"0.0.0.0/0"
]If the output still lists the previous ranges, check that each range in Public Access CIDRs is publicly routable, and then save the ranges again.
Next Steps
After deploying your EKS cluster, you may want to perform additional configuration tasks. Consider the following guides.